Adaptive Security Awareness Training
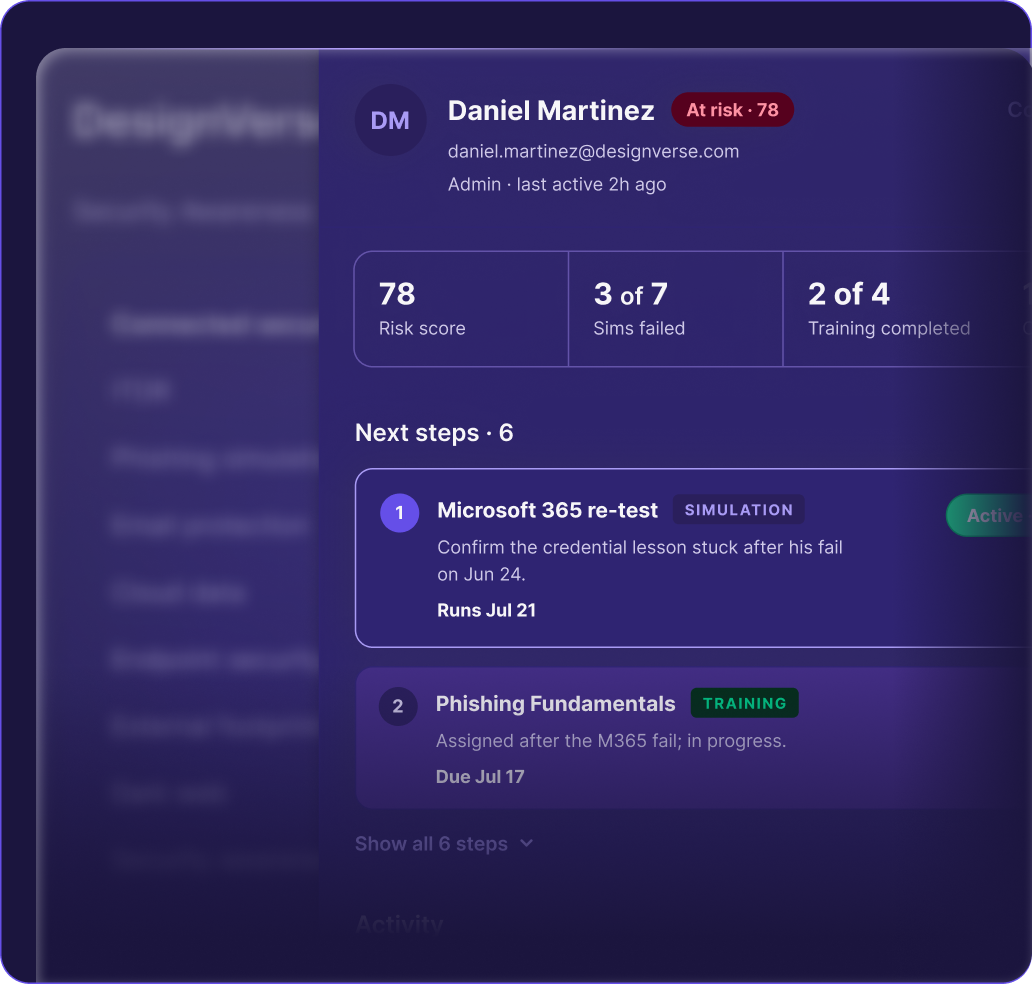
Most awareness programmes run on a schedule and hope for the best. Addicnet runs adaptive training instead: what the security controls see in your workspace — a failed simulation, a risky click, an exposed credential — decides what each employee is trained on next.
Training driven by real risk, not a calendar.
Powered by Adaptive security awareness
Why awareness programmes stall.
Human error
Unsafe clicks, shared passwords and approved fraudulent requests remain the fastest route into a business.
Disconnected training
Traditional training sits apart from real security signals, so it never addresses what actually went wrong.
Generic content
Every employee receives the same modules regardless of role, exposure or past behaviour.
Manual overhead
Scheduling, reminders and follow-ups consume internal time and still get deprioritised.
Simulations that miss
Obvious test emails teach staff to spot test emails, not the real attempt that imitates a supplier.
No evidence of progress
Completion is tracked, improvement is not — which leaves nothing useful for audit or insurers.
From signal to response.
Assess
Security signals, exposure findings and previous results identify each user's risk and learning needs.
Plan
Individual training plans combine role, compliance requirement and observed behaviour, not a single programme for everyone.
Deliver
Training and realistic simulations run on your schedule and language settings, with reminders handled automatically.
Adapt
New results reshape what comes next, and repeated failures increase simulation frequency for that user.
What is included.
- Personalised training plans per employee
- Adaptive phishing simulations based on real service patterns
- Content in more than 70 languages
- Automated scheduling, reminders and escalation
- Per-user risk scoring and programme health reporting
- Compliance-ready completion and results exports
What changes for your business.
Effort goes where risk is
Users who fail a simulation or show exposure are trained first, instead of everyone repeating the same module.
Administering it takes minutes
Plans and reminders run themselves, so nobody has to chase completion lists each quarter.
Evidence for compliance
Completion, simulation outcomes and outstanding assignments are reportable in a form auditors and insurers accept.
Controls that work alongside this one.
Email Security
API-based protection against phishing, impersonation and business email compromise, connected to the identities behind the inbox.
Explore controlBrowser Security
Block phishing, malicious extensions and data leaking into AI tools — inside the browser session, before anything is entered.
Explore controlExternal Footprint
See what attackers can see — exposed services, missing email records, certificate failures, leaked credentials and dark web activity.
Explore controlQuestions we are asked.
How long does each module take?
Most modules run five to ten minutes, designed to sit inside a working day. Frequency is agreed per group rather than set to a fixed annual cycle.
Can training fail staff or create HR issues?
Reporting is designed for security improvement, not performance management. Results are shared with the people you nominate, at the level of detail you choose.
Does it cover our compliance framework?
Plans can be aligned to the frameworks that apply to you, and completion evidence is exported for audits. We do not claim certification on your behalf.
Let's simplify your cloud infrastructure.
Tell us about your business and infrastructure requirements. Our team will assess your needs, recommend an approach and prepare a proposal.