External Footprint
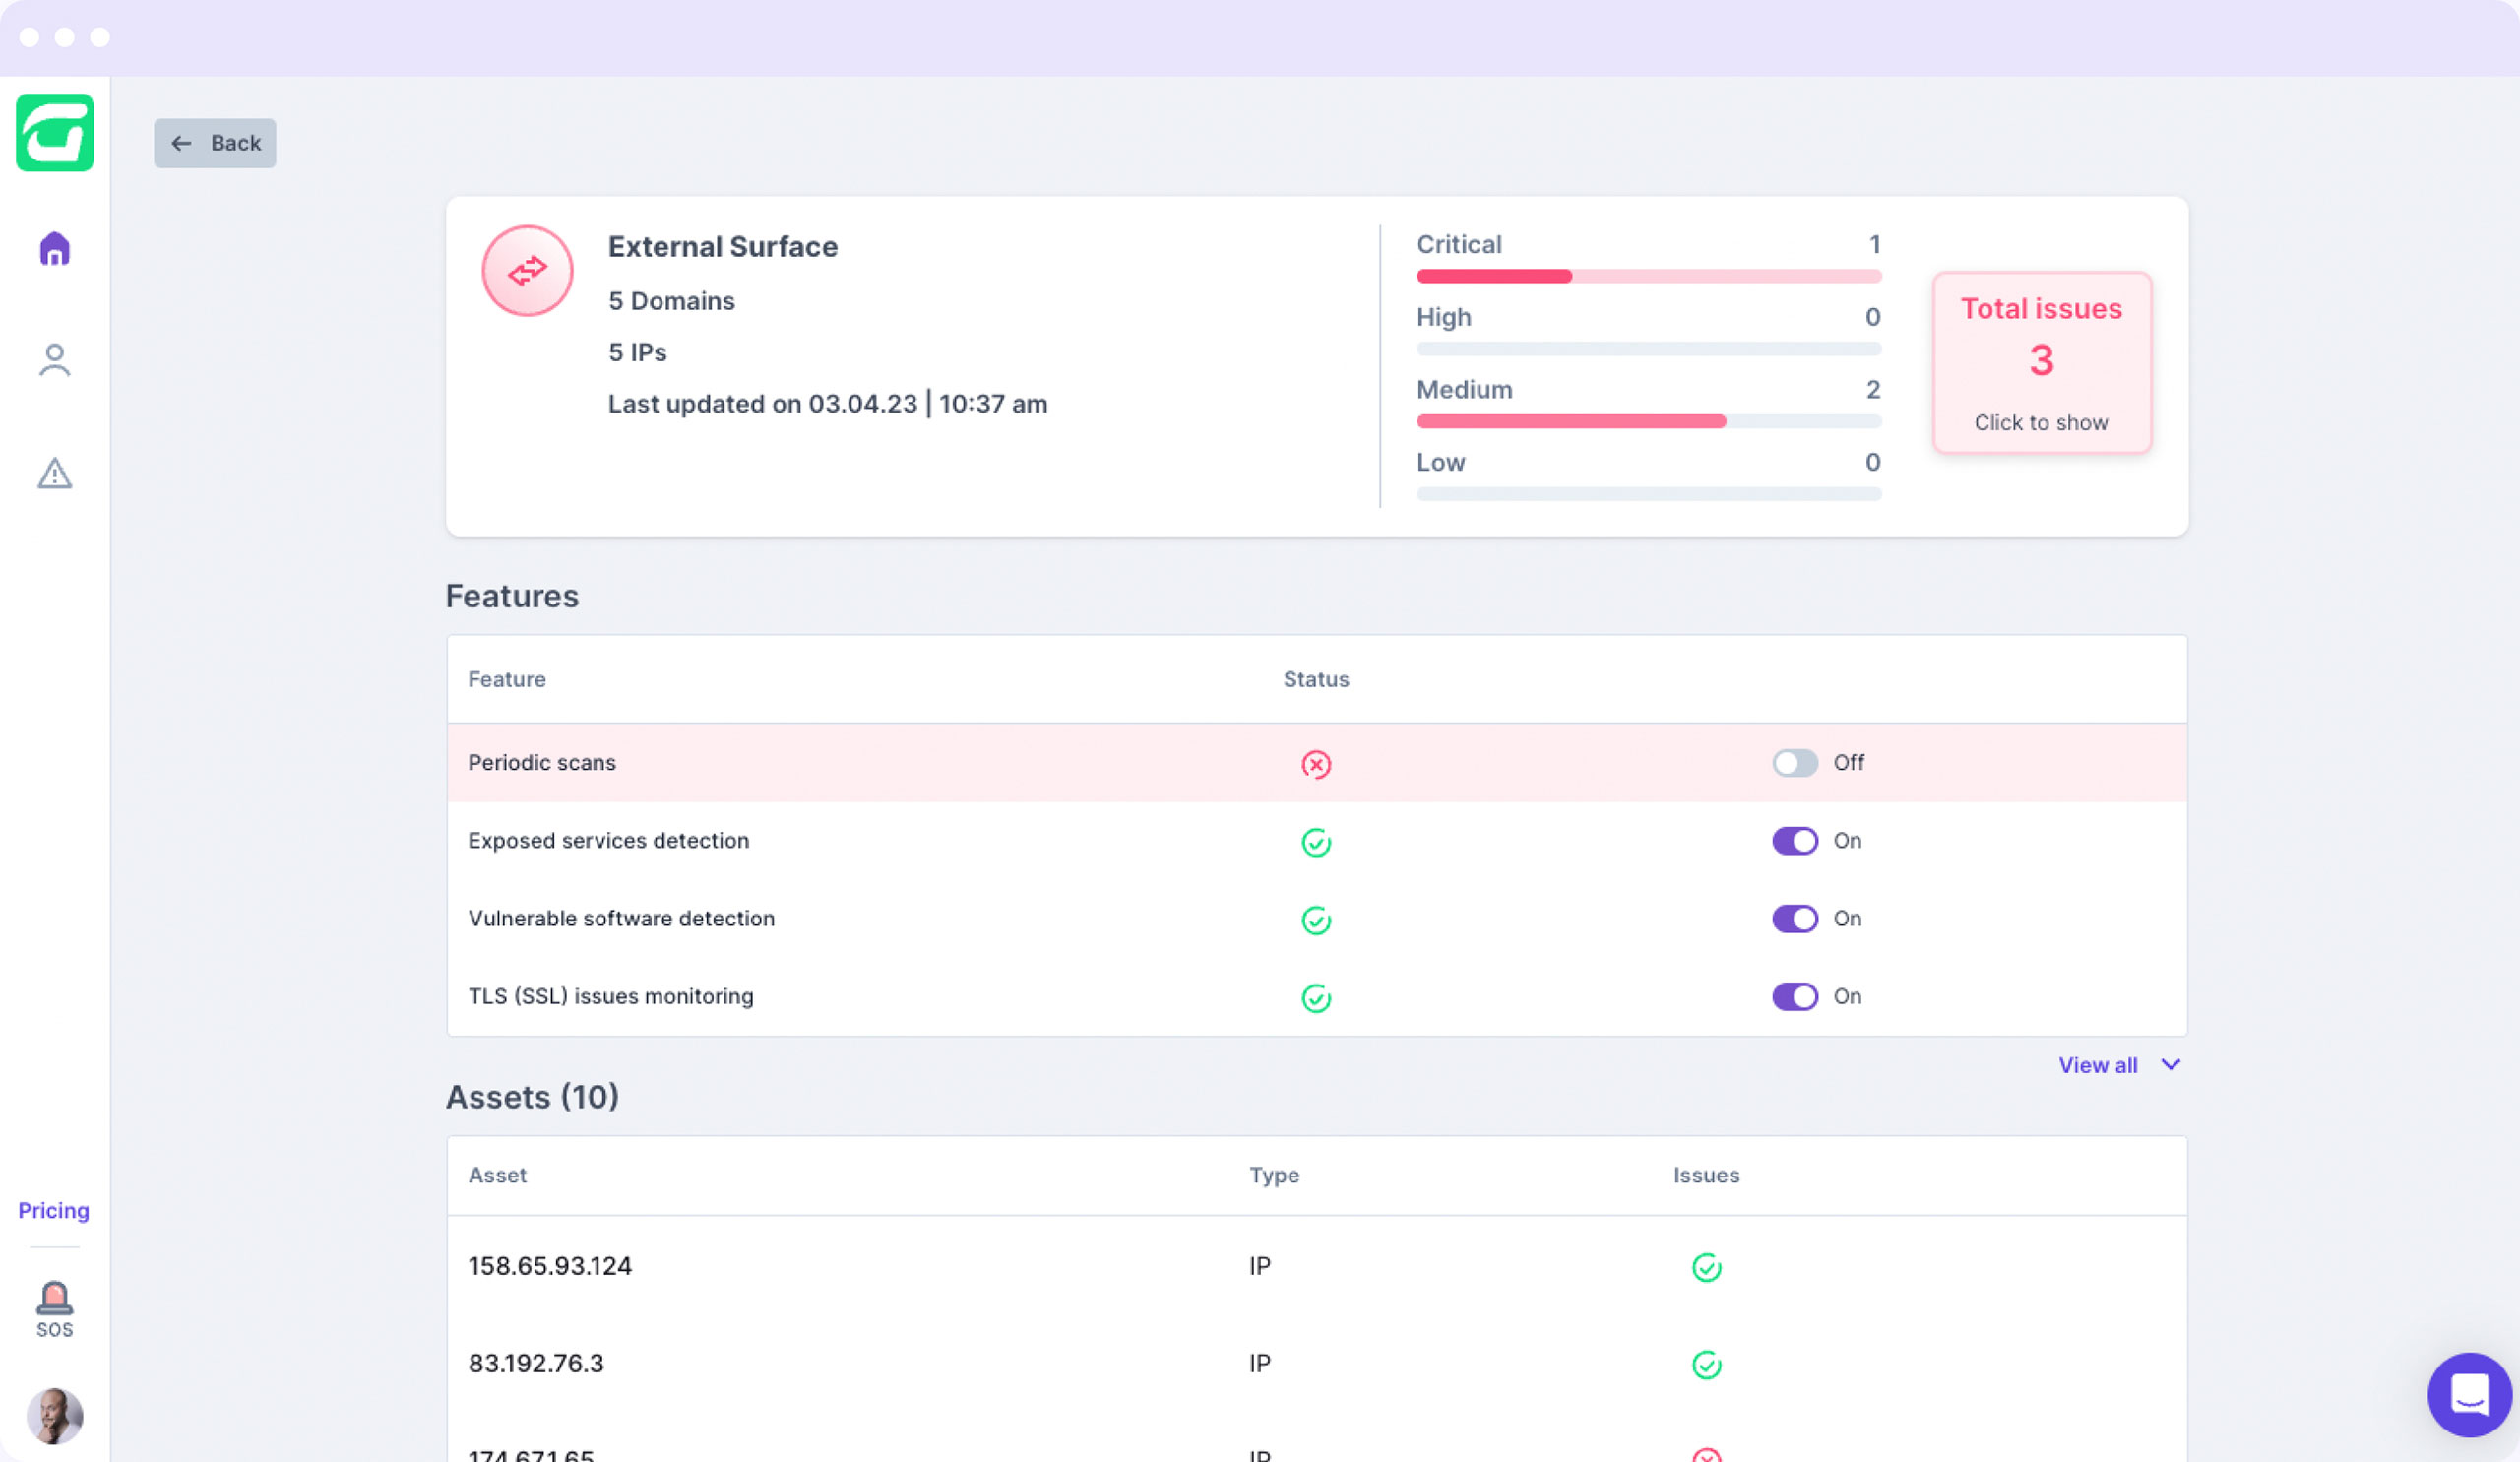
Your exposure is not only what you know you run. Addicnet continuously scans your domains, public-facing services, email authentication records and certificate chain, and monitors the dark web for credentials tied to your staff — then hands you remediation steps, not a raw list of findings.
Secure the perimeter from the outside in.
Powered by External footprint + dark web
What attackers find before you do.
Exposed services
Open ports, misconfigured firewalls and outdated applications that offer a route into your network.
Missing email records
Incorrect DNS, or missing SPF, DKIM and DMARC records, which invites spoofing of your own domain.
Invalid chain of trust
Expired or misconfigured TLS certificates that break trust and enable man-in-the-middle attacks.
Leaked credentials
Staff credentials circulating in data dumps and dark web marketplaces, ready to be tried against your systems.
Business targeting
Your organisation and its people named in forums where access and data are bought and sold.
Slow-moving drift
A changing estate adds new exposure every month, and nobody has a current picture of the outside view.
From signal to response.
Initiate
A baseline assessment starts from your business domains, with periodic rescans scheduled from day one.
Dark web results
Credential and data-leak findings usually arrive within minutes, and are alerted immediately when they matter.
External surface results
Public exposure scanning completes across the following hours to days, prioritised by severity and asset.
Remediate
Each issue carries a remediation playbook, and the security score updates as fixes are confirmed.
What is included.
- External service and open-port scanning
- SPF, DKIM and DMARC record monitoring
- TLS/SSL certificate and protocol review
- Dark web and leaked-credential monitoring
- External footprint assessment reporting
- Continuous security scoring and remediation playbooks
What changes for your business.
The attacker's view, on record
You see your public exposure the way it is probed from outside, documented and tracked over time.
Leaked credentials surfaced early
Exposed staff credentials are found and forced to reset before they are tried against your mailboxes.
Fixes, not just findings
Every issue arrives with a remediation path and an owner, so the list gets shorter instead of longer.
65%
of spear phishing attacks originate from leaked credentials bought on the dark web
Controls that work alongside this one.
Identity Threat Detection & Response
Detect account takeover across Microsoft 365 and Google Workspace, then revoke sessions and suspend users automatically.
Explore controlEmail Security
API-based protection against phishing, impersonation and business email compromise, connected to the identities behind the inbox.
Explore controlAdaptive Security Awareness Training
Training and phishing simulations built around each employee's real risk, delivered automatically and reported for audit.
Explore controlQuestions we are asked.
Do you need access to our network?
No. External footprint assessment runs from the outside, using only publicly available information about your domains and public-facing assets.
How often are scans run?
Dark web monitoring is continuous. External scans run periodically by default, with the cadence increased while remediation of critical findings is in progress.
Is this a penetration test?
No. This is continuous external exposure assessment. Where formal penetration testing or red-team work is required, we coordinate it with specialist providers.
Let's simplify your cloud infrastructure.
Tell us about your business and infrastructure requirements. Our team will assess your needs, recommend an approach and prepare a proposal.