Endpoint Security
Ransomware, zero-day exploits, supply chain attacks and fileless malware are built to get past signature-based antivirus. Addicnet deploys AI-powered endpoint detection and response across your devices, then runs it as a managed service — detection, triage, enrichment, containment and 24/7 response.
Stop endpoint threats before they move.
Powered by SentinelOne EDR
The threats an antivirus misses.
Crypto & locker ransomware
Attacks that encrypt files or lock devices, then demand payment to restore access.
Fileless & living-off-the-land
Threats that run in memory or abuse trusted system tools so nothing is ever written to disk.
Zero-day exploits
Attacks that exploit unpatched vulnerabilities to gain access, escalate privileges or execute code.
Traditional malware
Viruses, trojans and spyware that compromise devices, capture credentials and disrupt operations.
Advanced persistent threats
Targeted intrusions that keep access, move laterally and steal data while avoiding detection.
Supply chain attacks
Trusted software and update channels used to deliver malicious code into your estate.
From signal to response.
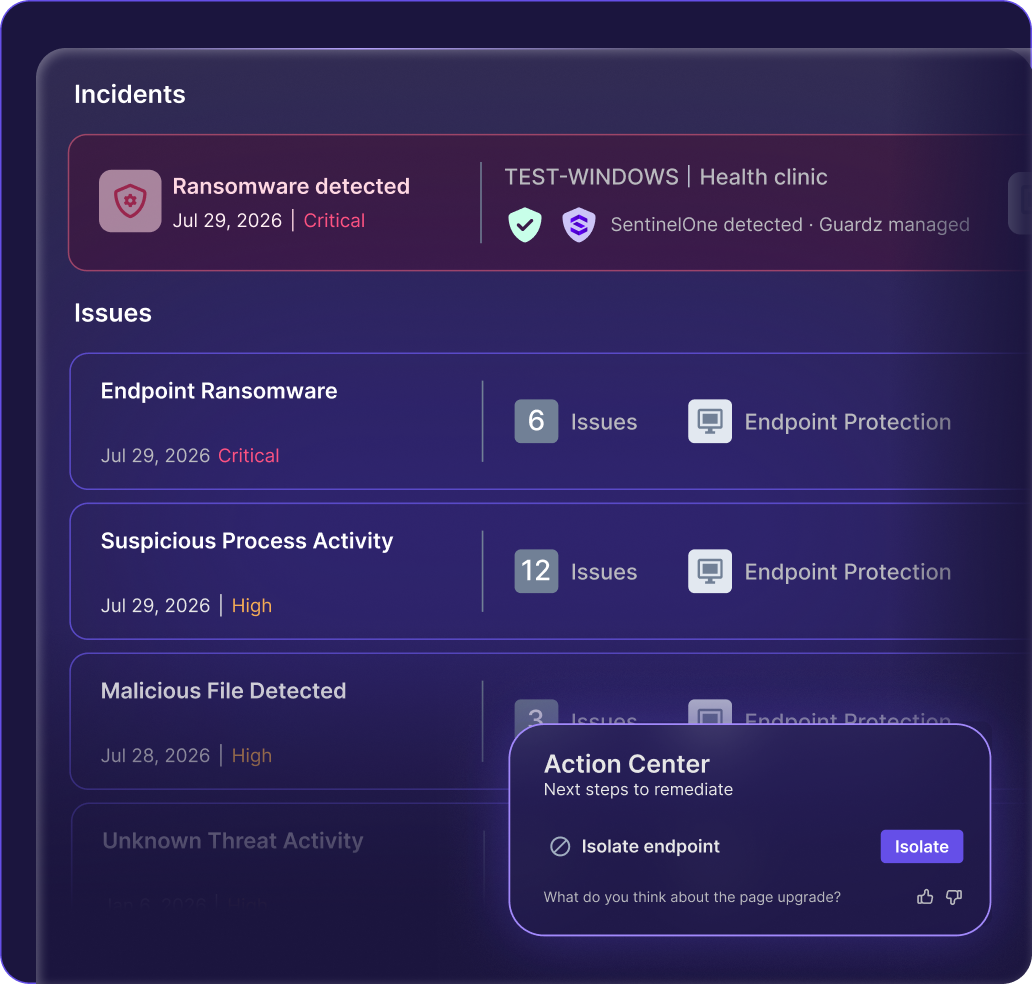
Detect
Behavioural and static AI on the endpoint blocks malicious files, suspicious processes and ransomware behaviour as it develops.
Triage
Endpoint detections are ranked against identity, email and browser signals, so the alert that matters reaches you first.
Enrich
Device details, MITRE ATT&CK mapping and threat intelligence establish scope and severity before anyone acts.
Respond
Response playbooks isolate the device and contain the threat at machine speed, with 24/7 analysts handling the cases that need judgement.
What is included.
- Agent provisioning across your Windows and macOS devices
- AI-driven EDR with behavioural and static analysis
- Managed antivirus through Microsoft Defender policies
- Automated endpoint isolation and threat containment
- MITRE ATT&CK and threat-intelligence enrichment
- 24/7 managed detection and response coverage
What changes for your business.
Containment in minutes, not days
An infected device is isolated automatically, so encryption and lateral movement stop before they reach file shares.
Context, not raw alerts
Endpoint findings arrive attached to the user, mailbox and session behind them — one incident to investigate, not four.
Coverage you do not have to staff
Analyst-level triage and response run around the clock, without building a security operations team of your own.
Controls that work alongside this one.
Identity Threat Detection & Response
Detect account takeover across Microsoft 365 and Google Workspace, then revoke sessions and suspend users automatically.
Explore controlEmail Security
API-based protection against phishing, impersonation and business email compromise, connected to the identities behind the inbox.
Explore controlBrowser Security
Block phishing, malicious extensions and data leaking into AI tools — inside the browser session, before anything is entered.
Explore controlQuestions we are asked.
Does this replace our existing antivirus?
In most environments it does. Endpoint protection is delivered with a modern EDR agent and managed Microsoft Defender policies, and the legacy antivirus is retired once the new agent is verified across the estate.
Which devices are covered?
Windows and macOS endpoints — laptops, desktops and servers running your business workloads. Coverage is agreed during onboarding so every device in scope has the agent before the service goes live.
What happens when a device is isolated?
The device loses network access except for the management channel, which stops ransomware and lateral movement immediately. You are notified with the evidence, and the device is released once it is cleaned and validated.
Let's simplify your cloud infrastructure.
Tell us about your business and infrastructure requirements. Our team will assess your needs, recommend an approach and prepare a proposal.